Know who has access. Prove you reviewed it.
DataBee User Access Review helps GRC and identity teams launch access review programs without the cost, complexity, and deployment effort of a full identity governance platform. Reviewers receive the context they need to make evidence-based access decisions, not rubber-stamp approvals.
User access reviews built for the applications traditional IGA platforms miss.
DataBee User Access Review provides a lightweight, purpose-built way to connect identity data from identity providers, central provisioning systems, legacy and custom applications, and mainframes. Launch campaigns quickly and maintain a complete audit trail while extending review coverage to the systems most organizations struggle to include.
Launch access review campaigns across modern and legacy applications from a single workflow.
DataBee UAR draws on the data that enterprises already have in their identity systems, integrating full user and business context to ensure that you're making decisions based on evidence instead of rote approvals.
Bring your identity data together.
Connect to your existing identity and access management providers and assemble the campaign population automatically. Every in-scope user-application pair is included and deduplicated, regardless of how access was granted—no data migration required.
Ingest data from hard-to-reach applications.
Bring legacy, mainframe, and custom applications into review scope through DataBee's custom ingestion, mapping, normalization, and correlation capabilities.
Integrate business context into all access decisions.
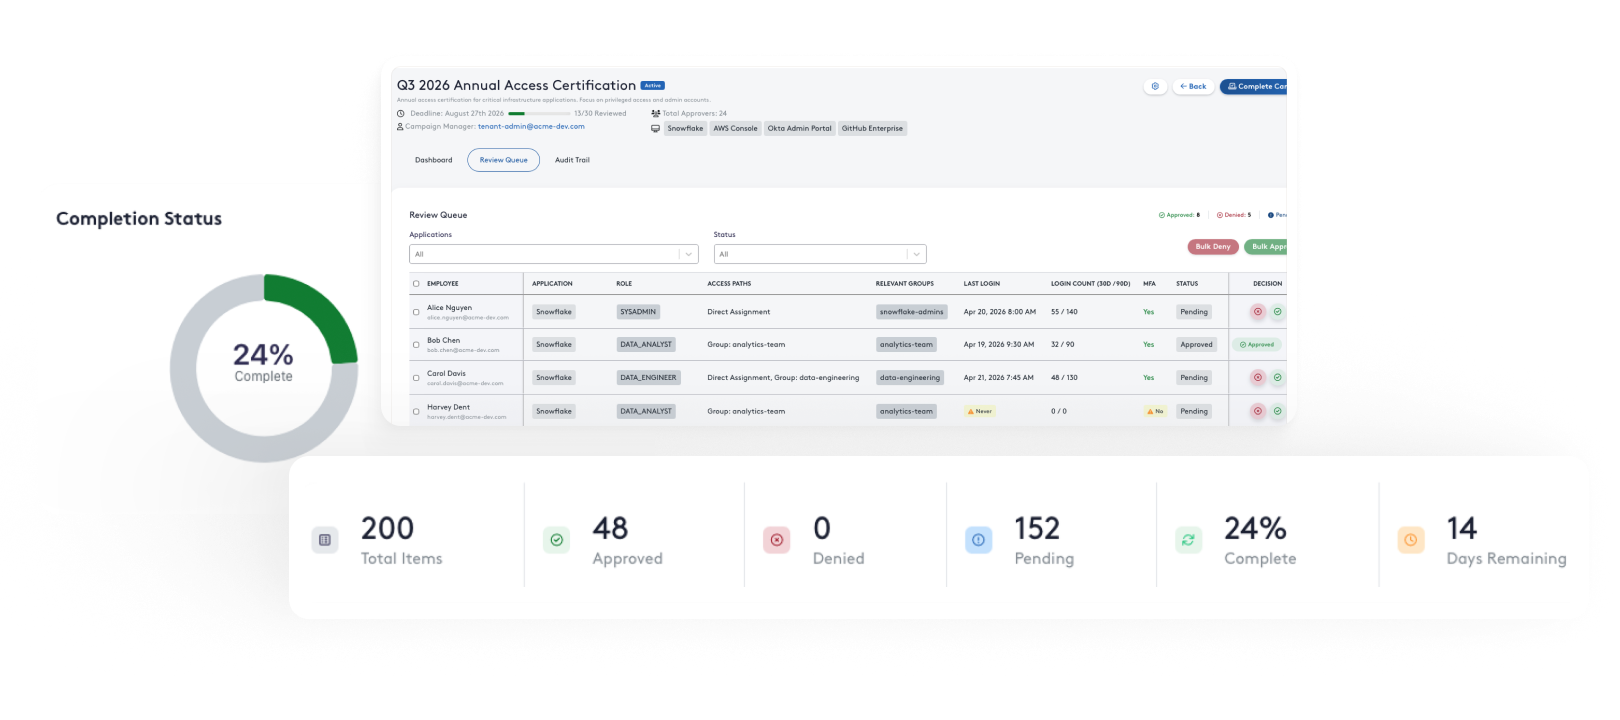
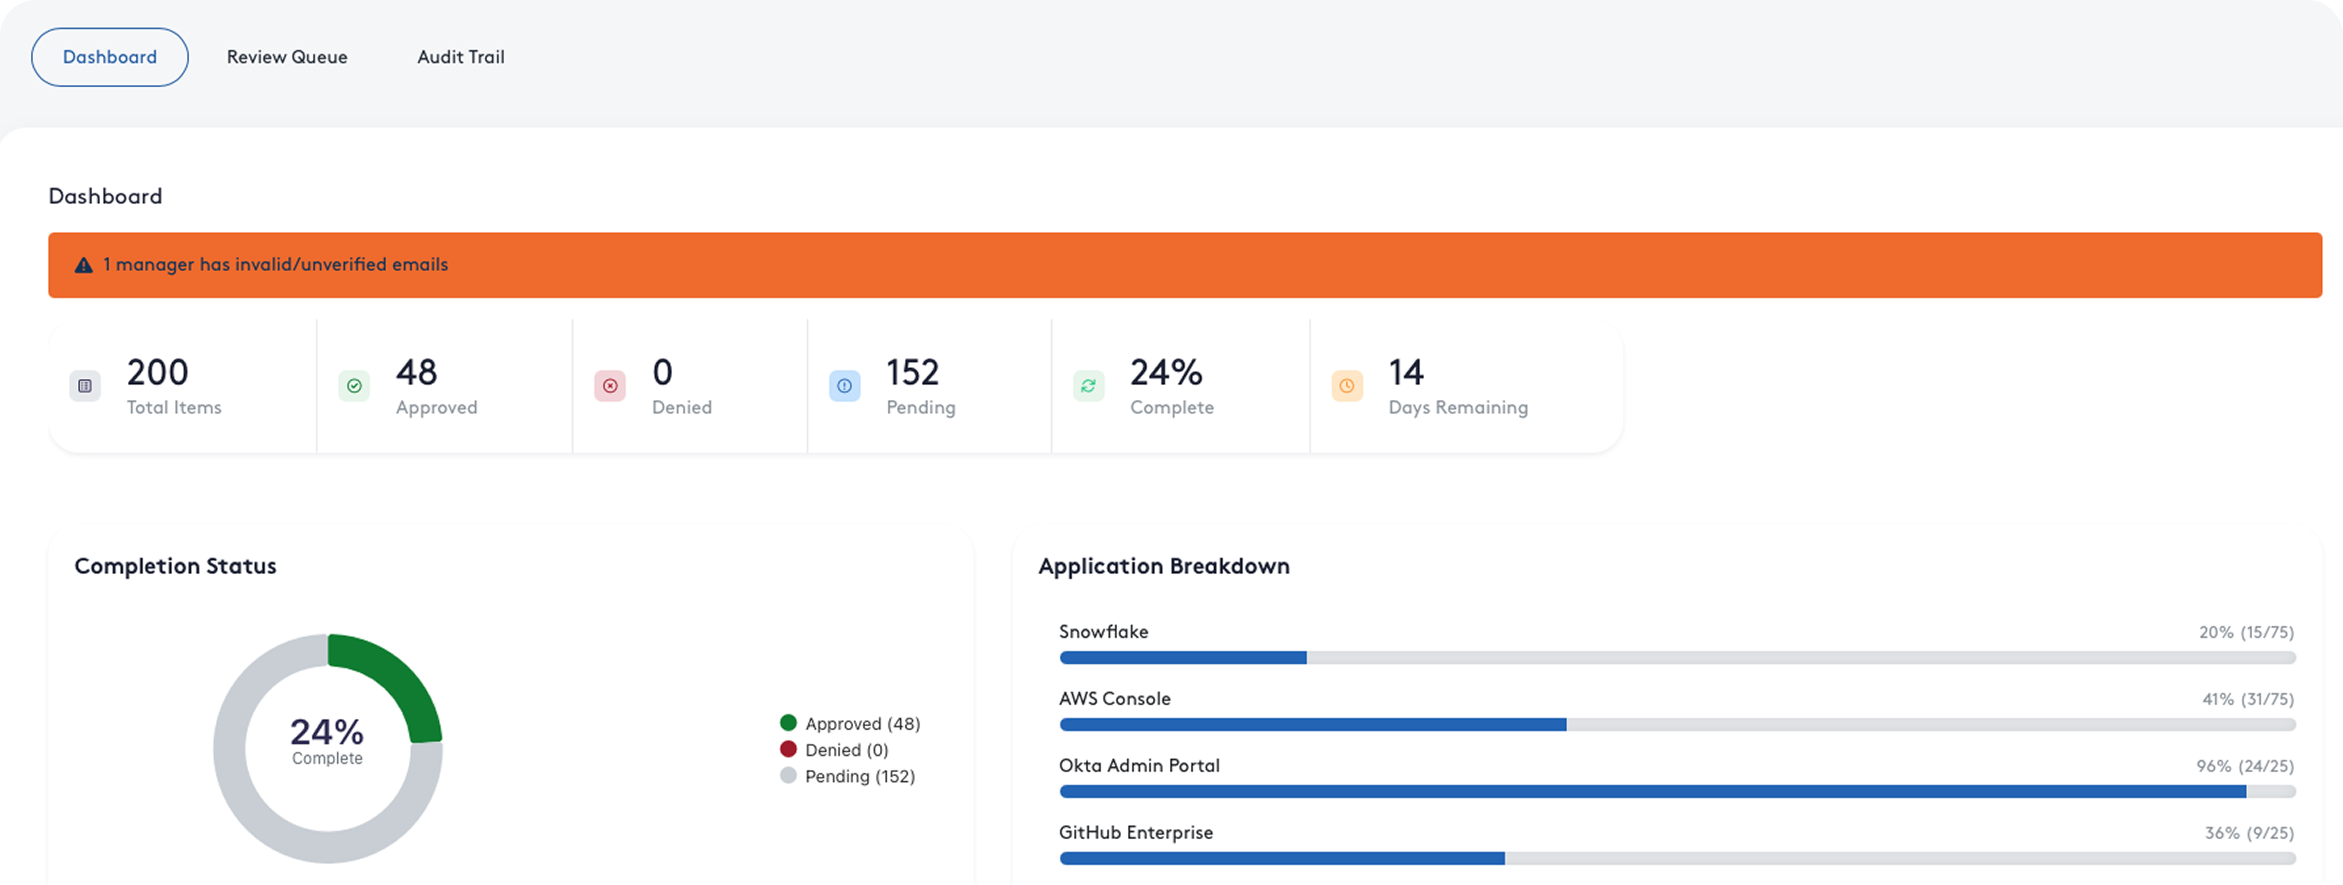
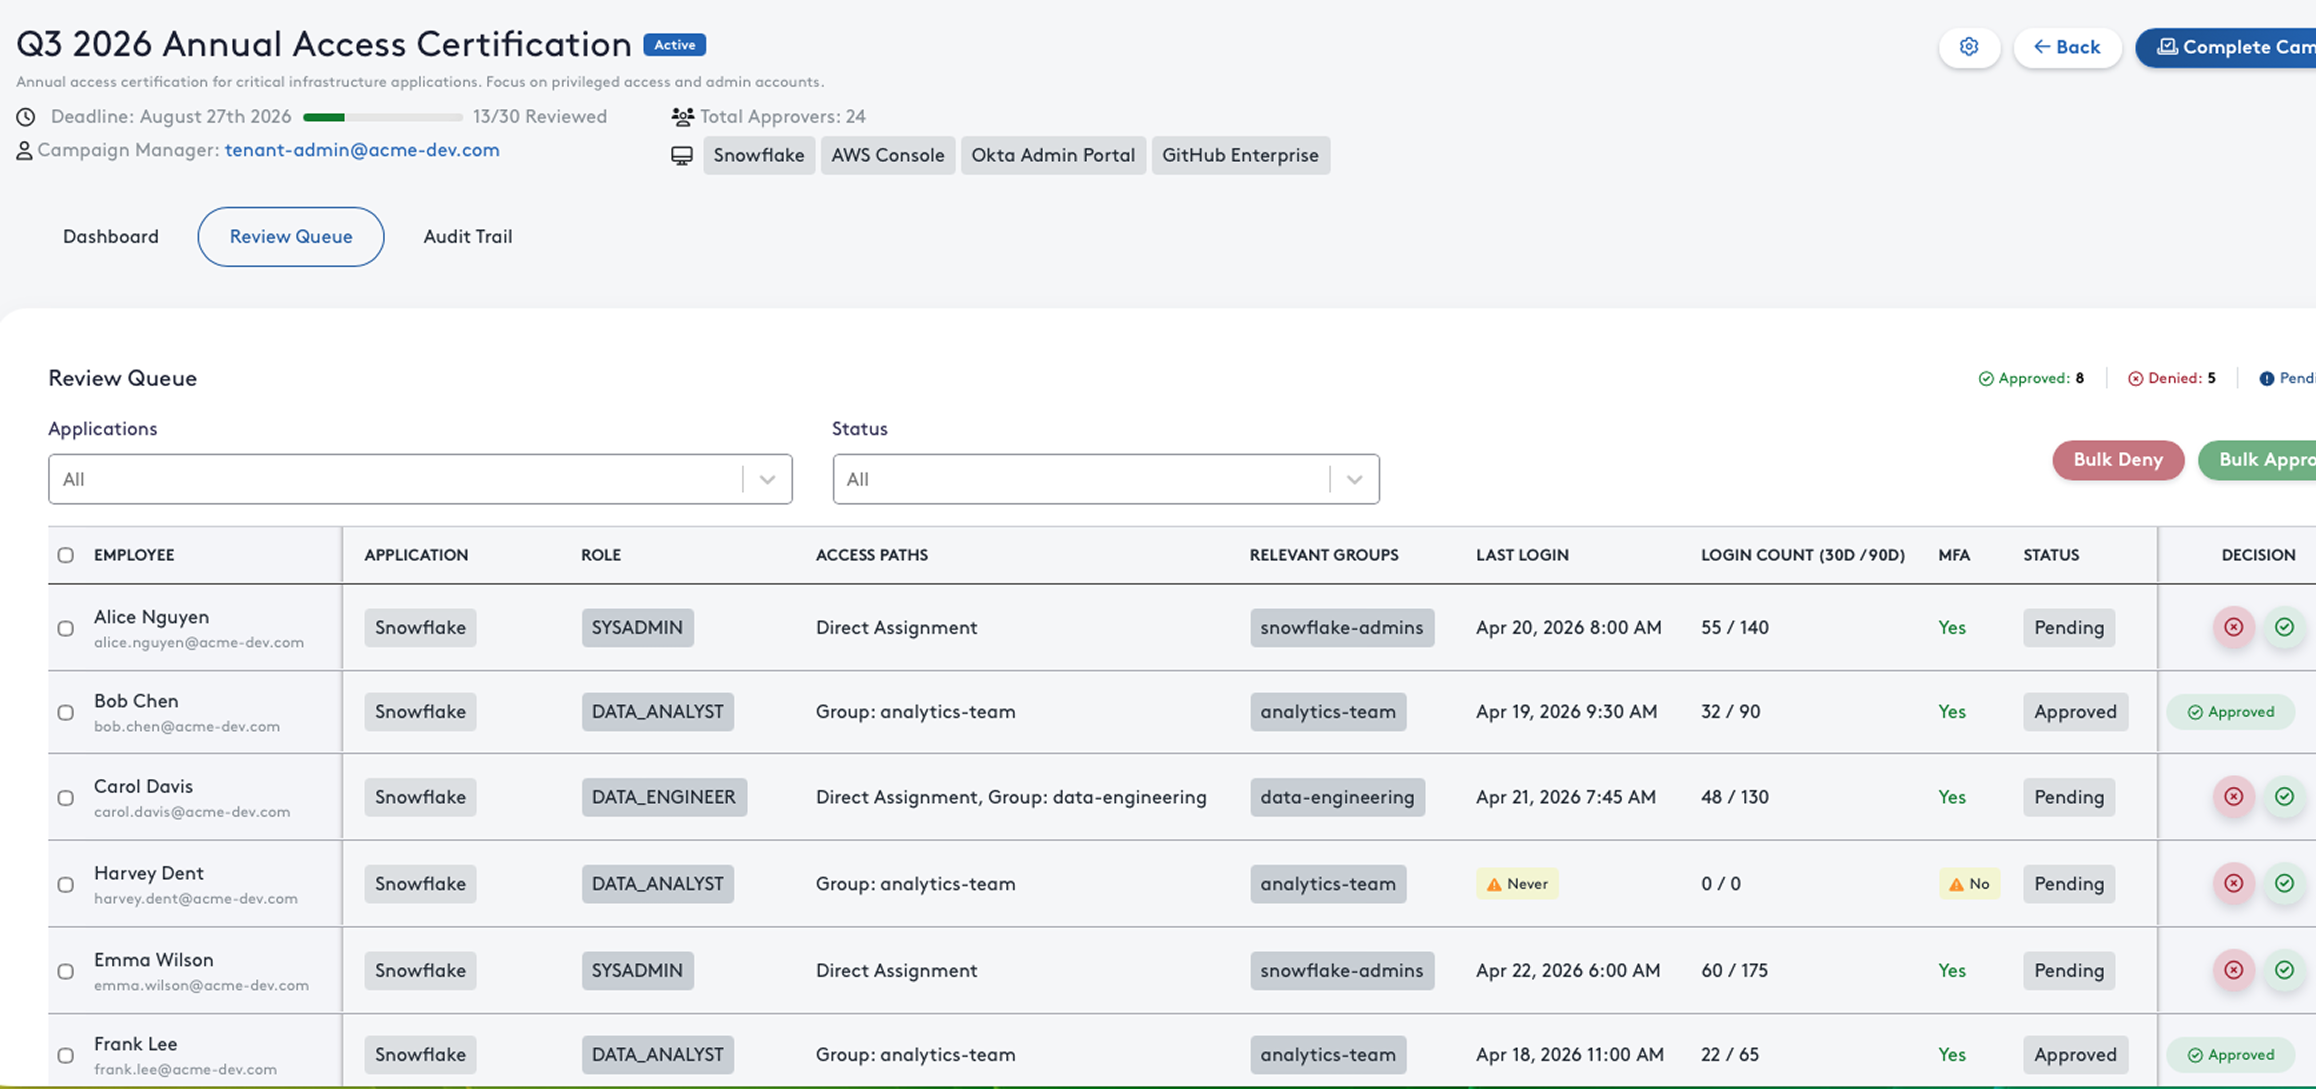
Access decisions route to each user's direct manager via their existing SSO. Managers see last login, login frequency, MFA status, and access context on every item. Admins track completion across the full organizational hierarchy and dispatch bulk reminders from a single dashboard.
Resolve access decisions in one centralized workflow.
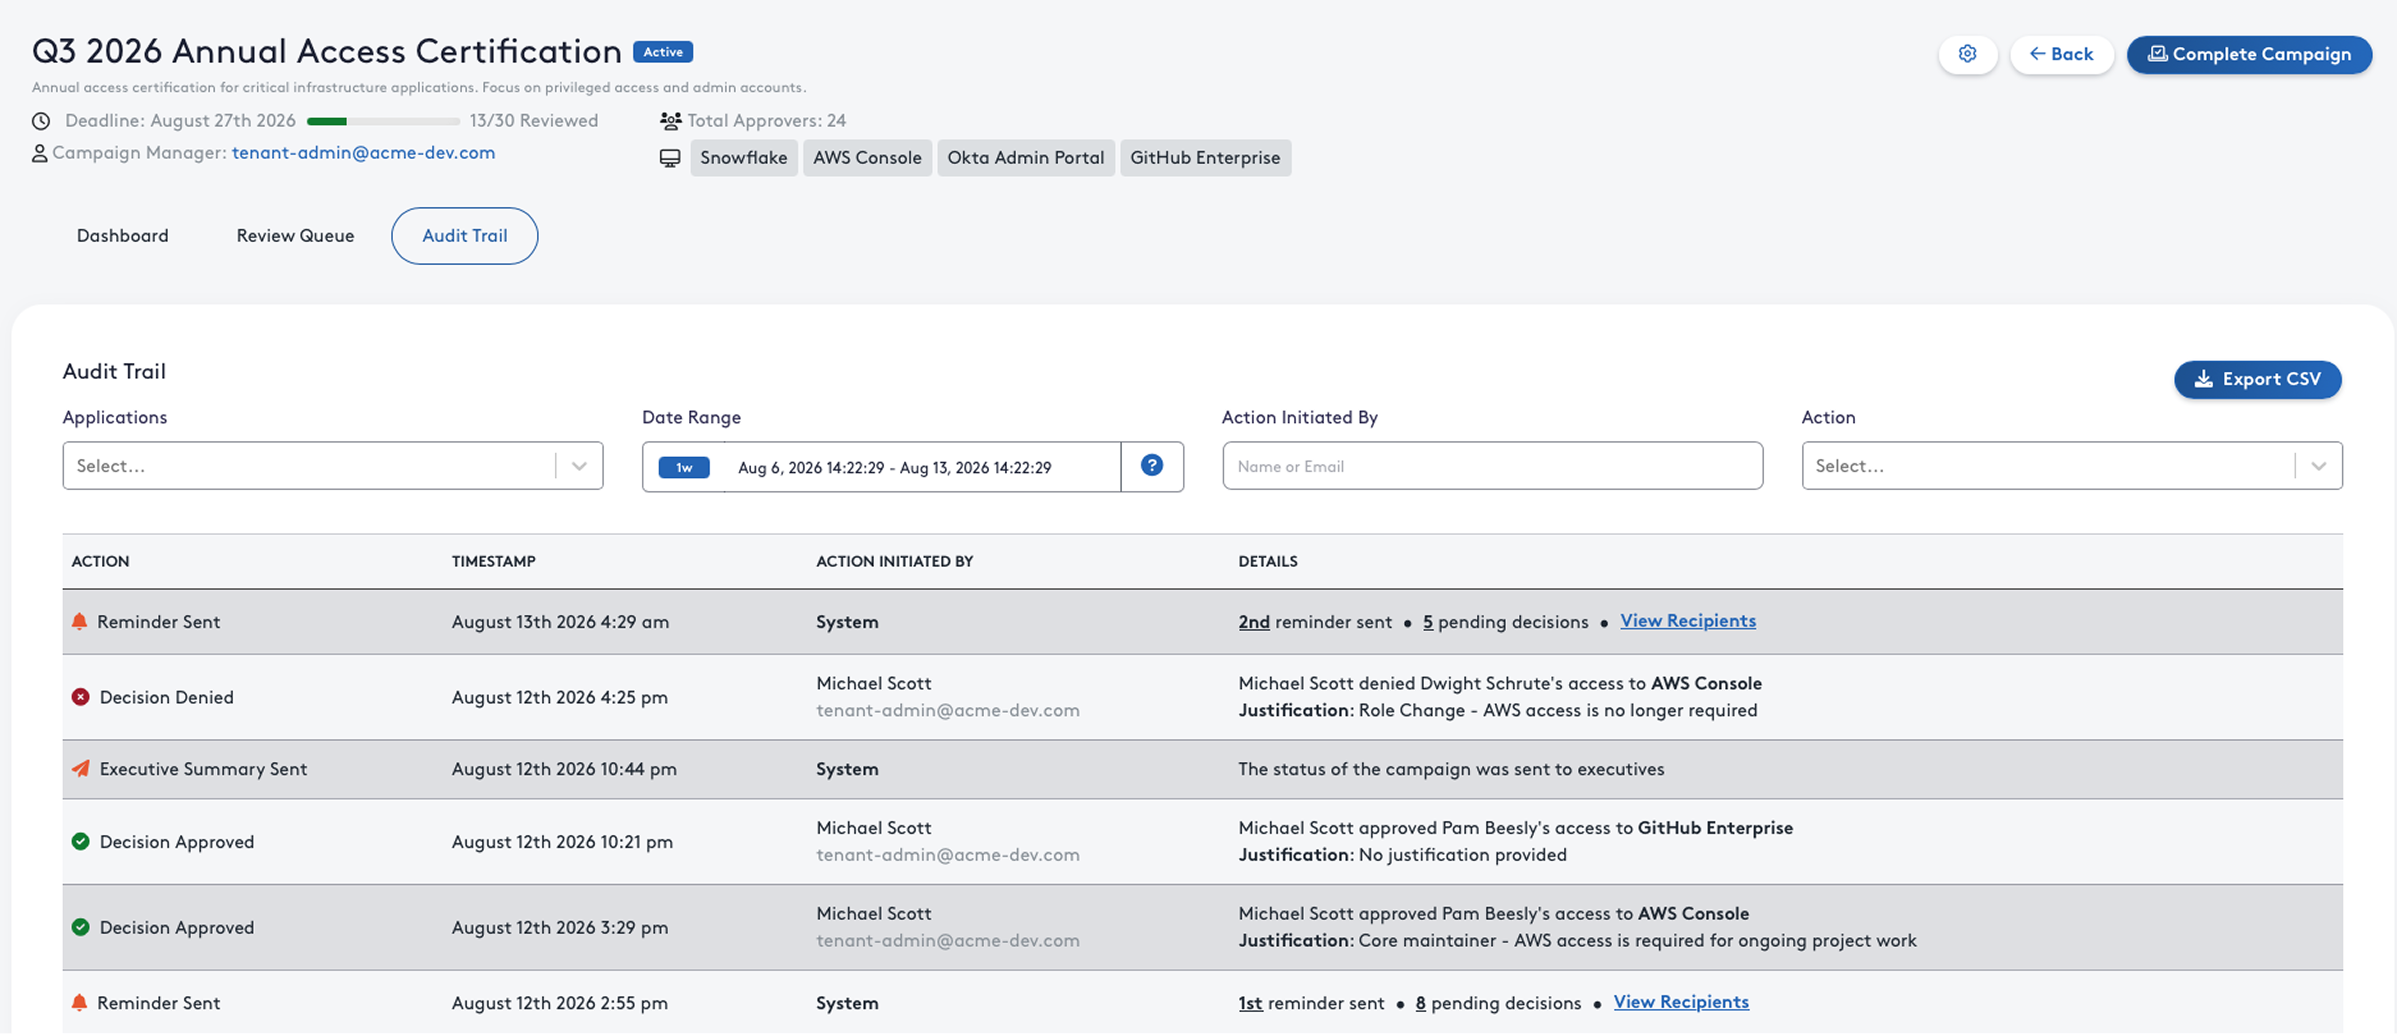
On campaign close, denied access is grouped by application and orchestrated as remediation workflows. The full decision record, including every approval, denial, escalation, and notification, is retained and exportable for compliance reporting.
User access reviews from the same trusted cyber context layer.
Everything required to streamline the access review process.
Unified visibility into user entitlements across every in-scope application.
Identity data ingested from everywhere means you have clear insight into which users have access to which tools, including apps that IGA tools miss.
True auditable record of access reviews.
Access review campaigns are managed in-platform on manual or scheduled timelines, complete with audit trail for compliance reporting.
Reduce reviewer fatigue and eliminate duplicate effort.
No more cross-checking to ensure access got removed from everyone; one denial cuts off every pathway to login.
True business context with every review.
Insight into every piece of information around user access, ensuring risk-informed and accurate decisions around who retains access to what.
Reviews routed to the right person every time.
The right person is always assigned the decision automatically, regardless of application.
Complete visibility into progress and reporting.
Teams can report on access review progress from one single dashboard while also ensuring reminders are sent out regularly.
Seamless integration with existing processes.
DataBee UAR works directly with tools already used to manage the work around removing denied access.
A user access review is the process of verifying that each person's access to applications, systems, and data is still appropriate for their role. Reviewers confirm or revoke access, and every decision is logged as evidence. Organizations run reviews on a regular cadence to keep access aligned with need and to support audits.
Most organizations review access quarterly or semi-annually, with more frequent reviews for privileged or high-risk systems. The right cadence depends on your regulatory requirements, the sensitivity of the application, and how often roles change. DataBee lets you schedule recurring campaigns at any cadence.
Identity governance is the practice of managing the full identity lifecycle, including provisioning, access requests, role management, and reviews. Identity governance & administration (IGA) solutions usually require extensive deployment time. A user access review is one specific control: periodically confirming that existing access is still appropriate. DataBee focuses on the review itself, so teams can run defensible access reviews — including for the legacy, custom, and mainframe apps IGA tools often miss — without deploying a full IGA suite.
Access certification is another term for a user access review: a reviewer certifies (confirms or revokes) that a user's access is still warranted. The certified decisions form an auditable record you can stand behind during compliance reviews.
DataBee can bring identity data into review scope from identity providers, central provisioning systems, and hard-to-reach sources such as legacy, custom, and mainframe applications with our custom ingestion, mapping, normalization, and correlation technology. That extends coverage to systems many IGA tools can't reach.
Frameworks and certifications such as SOX, SOC 2, and ISO 27001 expect organizations to periodically review and provide evidence for who can access critical systems. Running scheduled reviews with a traceable decision record helps demonstrate that access is monitored and controlled. DataBee retains every approval, denial, and escalation as exportable evidence as support for these reviews, not a replacement for your compliance program.
Get the clarity you need to manage cyber risk.
Schedule your 30-minute demo to see how DataBee's AI-powered technology turns your data into fast, clear, defensible control and cyber risk clarity.