Building Resilience with DORA: Strengthening Compliance and Operational Risk Management


Free the CISO, a podcast series that attempts to free CISOs from their shackles so they can focus on securing their organization, is produced by CIO.com in partnership with DataBee®, from Comcast Technology Solutions.
In each episode, Robin Das, Executive Director at Comcast under the DataBee team, explores the CISO’s role through the position’s relationship with other security stakeholders, from regulators and the Board of Directors to internal personnel and outside vendors.
Navigating new compliance frameworks can be daunting. In this webinar, Tom Schneider and Annick O’Brien discuss the EU’s Digital Operations Resilience Act (DORA) – a regulation designed to strengthen operational risk management. Discover how DORA’s principal-based approach helps organizations to prepare for incidents, manage 3rd party risks, and build resilience.
Topics include:
- Why DORA is important and who it applies to
- 3rd Party Risk
- The 5 Pillars of DORA
- Principal-based legislation
- The influence of NIST CSF on DORA’s framework
Learn about how your organization can build resilience while navigating DORA.
Presented by:
- Tom Schneider, GRC Consultant, DataBee®, A Comcast Company
- Annick O’Brien, General Counsel, CybSafe
More posts

Learn how DataBee® streamlines deployments with flexible architecture, a powerful security data fabric, and intelligent asset discovery—delivering compliance and visibility whether or not your organization relies on a CMDB.

Discover how a security data fabric for compliance helps GRC teams unify data, improve audit readiness, and leverage AI for continuous control monitoring and faster remediation.
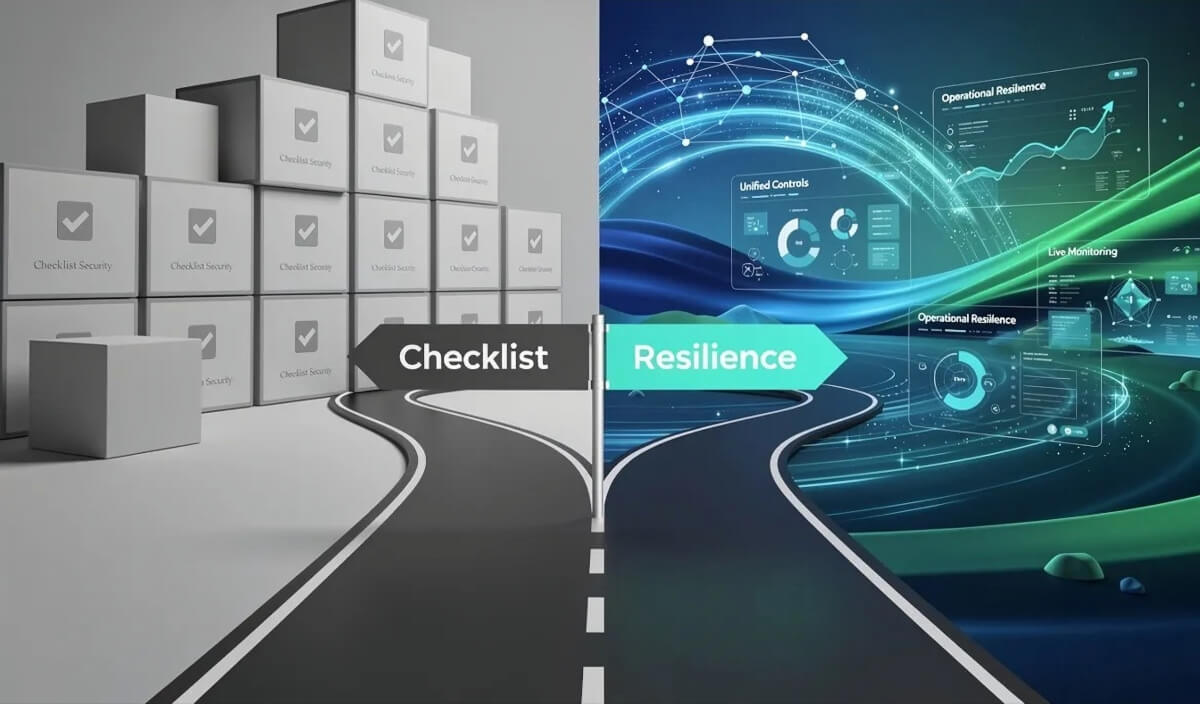
Regulated industries face rising threats and stricter rules. Explore why compliance alone isn’t enough—and how unified control data strengthens both security and resilience.
Get the clarity you need to manage cyber risk.
Schedule your 30-minute demo to see how DataBee's AI-powered technology turns your data into fast, clear, defensible control and cyber risk clarity.